
01
Understand software composition
Use a Software Bill of Materials (SBOM) and Software Composition Analysis (SCA) to connect CycloneDX component information and package identifiers (PURL) with vulnerability evidence.
WERANA / Services
Vulnerability analysis
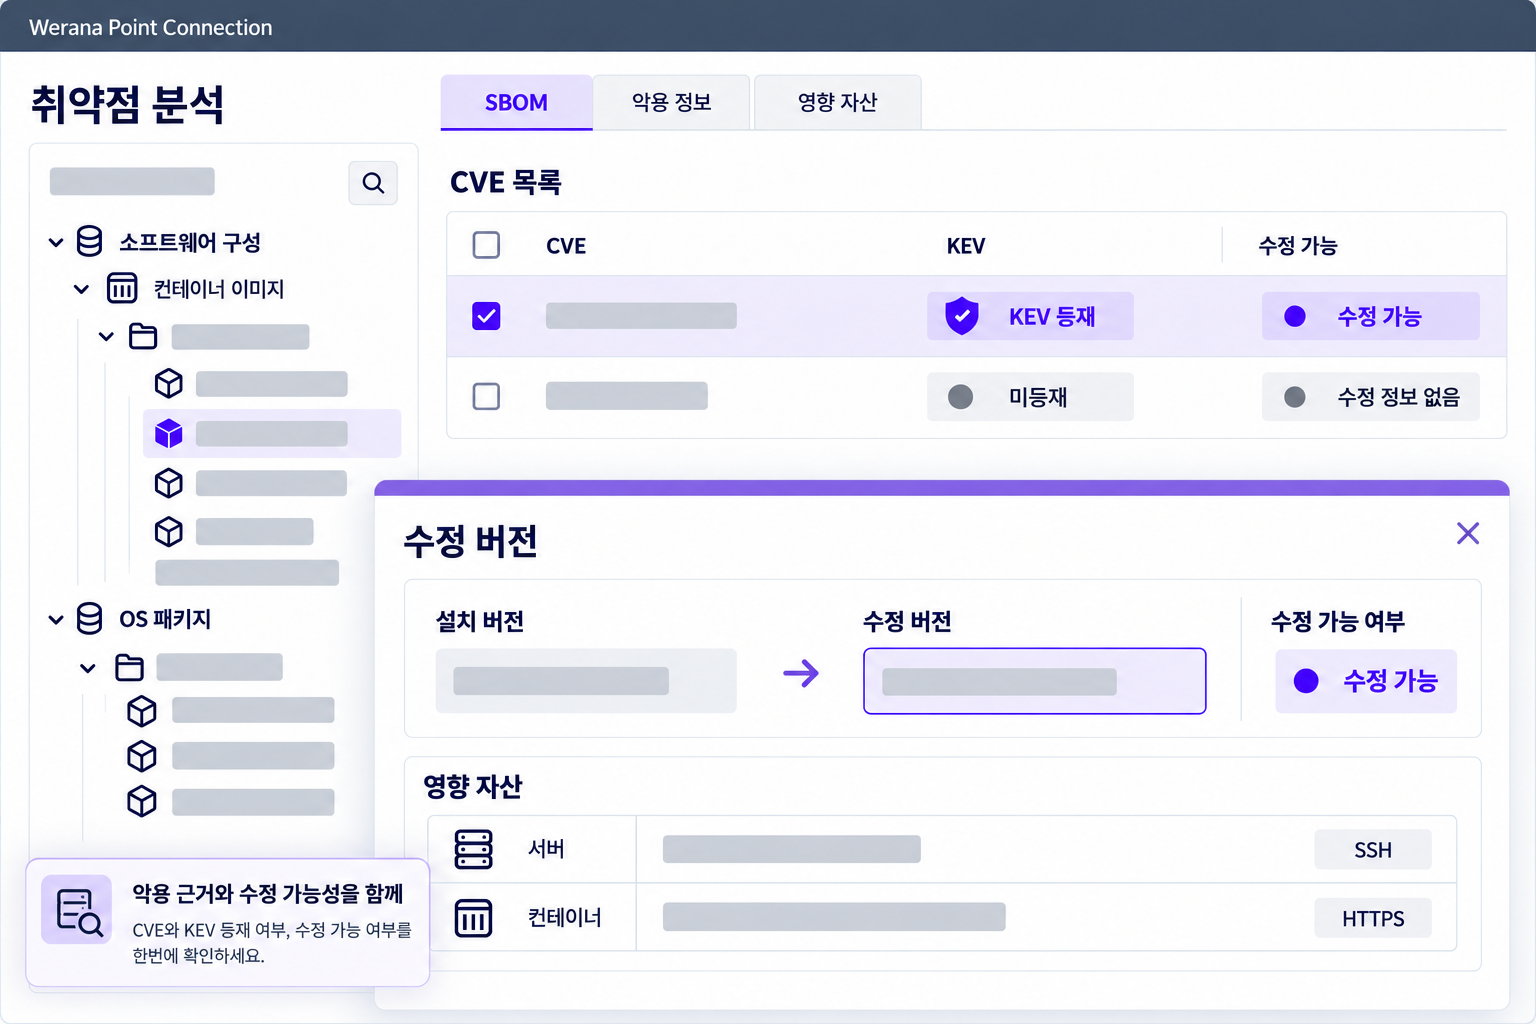
Analyze image and OS-package SBOM components alongside related CVEs, affected assets, exploitation signals, and fixed versions.
Review workflow
Look beyond vulnerability counts. Compare exploitation evidence and available fixes to focus remediation review.
01
Use a Software Bill of Materials (SBOM) and Software Composition Analysis (SCA) to connect CycloneDX component information and package identifiers (PURL) with vulnerability evidence.
02
Distinguish CVE identifiers, CVSS severity, EPSS exploitation probability and CISA KEV exploitation history. Review CWE weakness types and collected CPE product identifiers as supporting information.
03
For Vulnerability Management, compare installed and fixed versions, patch availability and affected assets. Distinguish CPE-based network-service and OS matching from precise package analysis when reviewing remediation.
Environment & coverage
Review the applicable scope based on your assets, collection permissions, and existing security operations.
Security categories to compareSCA · SBOM · SPDX · VEX · Vulnerability Management
Analysis covers collected container images and OS packages, subject to available vulnerability information.
FAQ
Review components, CVEs, and affected assets based on collected container images and OS packages.
SBOM describes software components; SCA analyzes them; and CycloneDX and SPDX are formats used for SBOMs. VEX communicates whether a vulnerability affects a specific product. Werana Point Connection describes CycloneDX-based image and OS-package analysis here. Confirm SPDX import and export, VEX processing and license-management coverage separately.
CVSS describes severity, EPSS predicts exploitation likelihood, and CISA KEV records known exploitation. Consider available indicators alongside affected assets, exposure and fixed versions. CWE, CPE and PURL identify weakness types, products and packages respectively. Missing scores do not establish safety.
Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.