
01
One view of your operating assets
Use Asset Inventory and Software Inventory to review servers, containers, Kubernetes resources and their collected software information.
WERANA / Services
Asset management
Organize servers, containers, and services, then review the management status and open services of discovered devices.
Review workflow
Discover devices and services beyond the managed inventory, then review their relationship to important business assets.
01
Use Asset Inventory and Software Inventory to review servers, containers, Kubernetes resources and their collected software information.
02
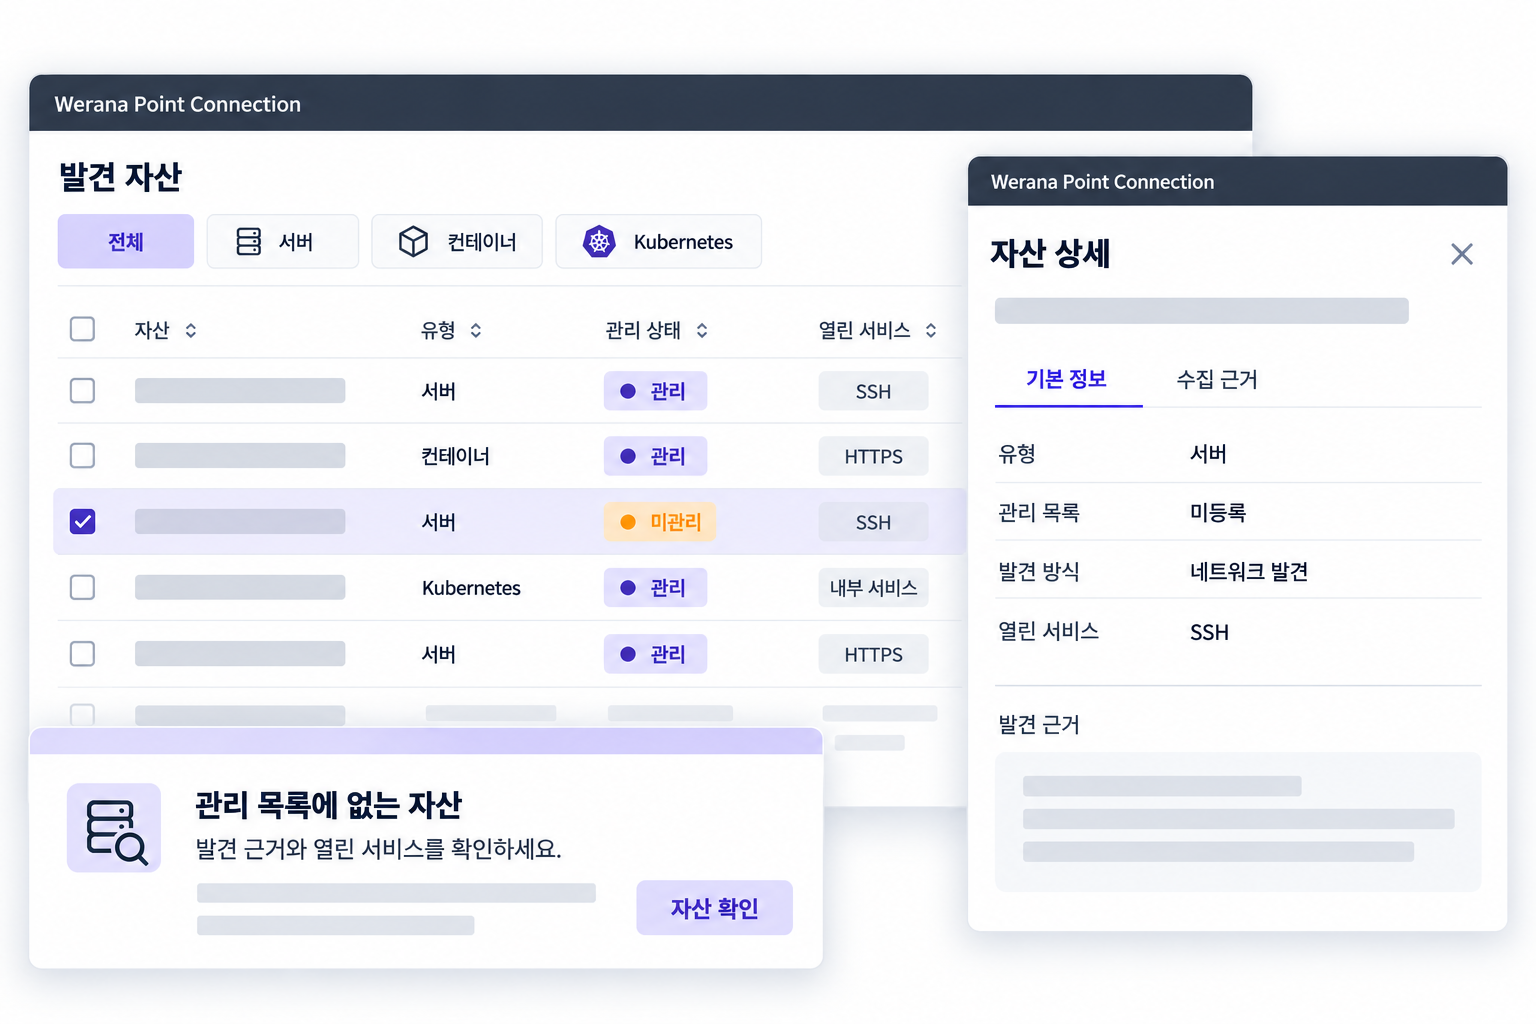
Review devices found through Asset Discovery, their management status, and open ports and services.
03
Use confidentiality, integrity and availability (CIA) ratings and N2SF asset grades to identify classification gaps.
Environment & coverage
Review the applicable scope based on your assets, collection permissions, and existing security operations.
Security categories to compareCAASM · EASM · ITAM · CMDB
Discovery depends on collection targets, scan ranges, and network conditions.
FAQ
Review management status and open services to identify assets that need investigation.
CAASM reconciles security assets across sources; EASM focuses on the external attack surface; ITAM covers IT asset lifecycles; and a CMDB manages configuration items and relationships. Review Werana Point Connection against your needs for collected asset and software inventories, network discovery and management status.
N2SF asset grades and classification rules help organize protection targets. Assigning a grade does not establish that every N2SF control is satisfied. Discovery and collection also depend on permissions, targets and network scope.
Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.