
01
Start with external exposure
Use an Attack Surface Management (ASM) perspective to review externally exposed assets and accessible services.
WERANA / Services
Attack surface & paths
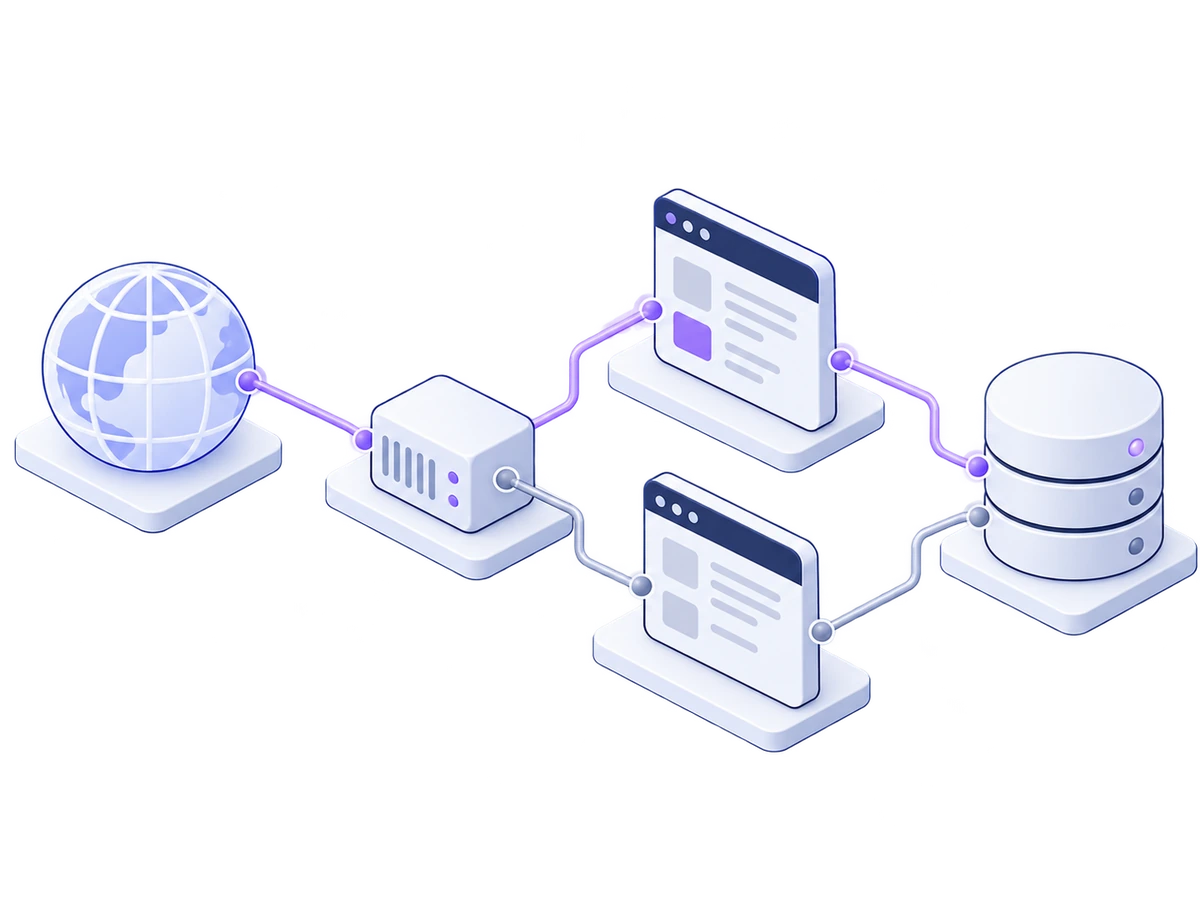
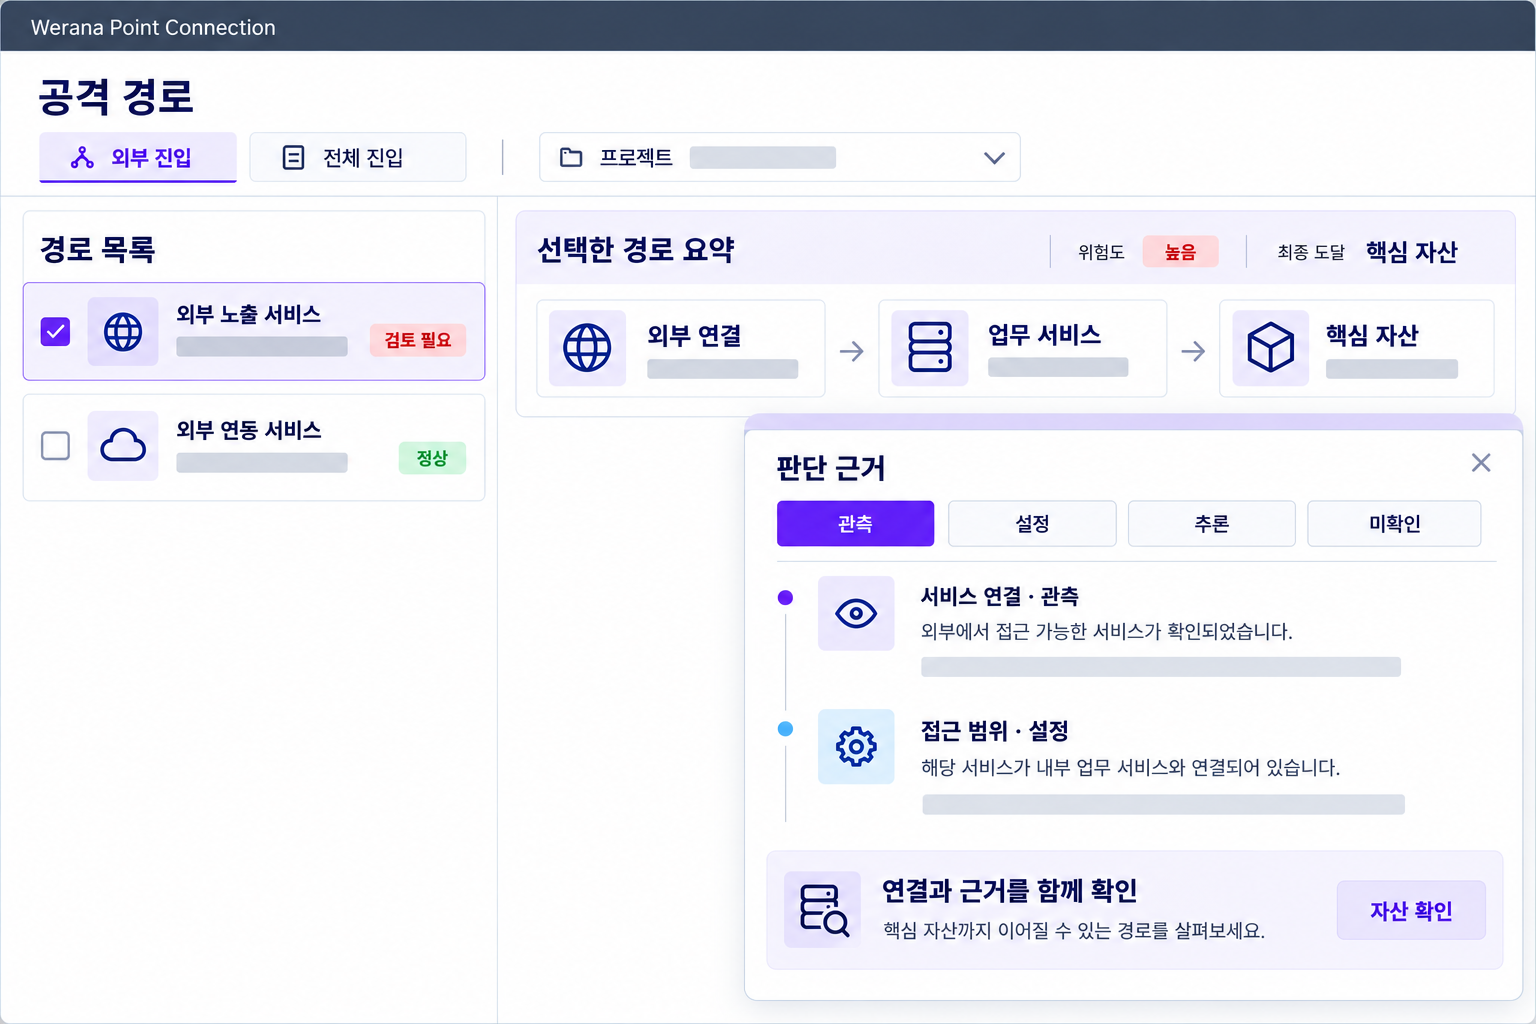
Follow exposed services and asset relationships, reviewing the evidence behind each path and the gaps that need further investigation.
Review workflow
Review potential connections to important services, together with the evidence behind each relationship.
01
Use an Attack Surface Management (ASM) perspective to review externally exposed assets and accessible services.
02
Review Network Topology and Service Dependency relationships as part of Attack Path Analysis.
03
Assess path priority while distinguishing observed, configured and inferred evidence from unverified segments.
Environment & coverage
Review the applicable scope based on your assets, collection permissions, and existing security operations.
Security categories to compareEASM · CAASM · CTEM · BAS
Available paths depend on collected relationships and enabled analysis capabilities.
FAQ
A path describes potential connections and their evidence. Its presence alone does not establish a breach.
EASM examines the externally visible attack surface; CAASM reconciles assets and security information across sources. This service reviews potential paths using collected external connections, services and critical-asset relationships. Confirm external discovery and integration coverage for your environment.
CTEM is an ongoing approach spanning exposure identification, prioritization, validation and remediation. BAS uses simulated attacks to validate controls. Reviewing potential paths here is separate from executing attacks or validating successful exploitation. A path alone does not establish a breach or successful attack.
Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.