Skip to content

WERANA / Services

Accounts & permissions

Review service-accountpermissions and credentials.

  • NHI
  • RBAC
  • ServiceAccount
  • RoleBinding
  • ClusterRole
  • ClusterRoleBinding
  • Least privilege
  • Long-lived tokens

Inspect Kubernetes service-account RBAC relationships, long-lived tokens, and observable credential-related signals.

Conceptual service illustration

Review workflow

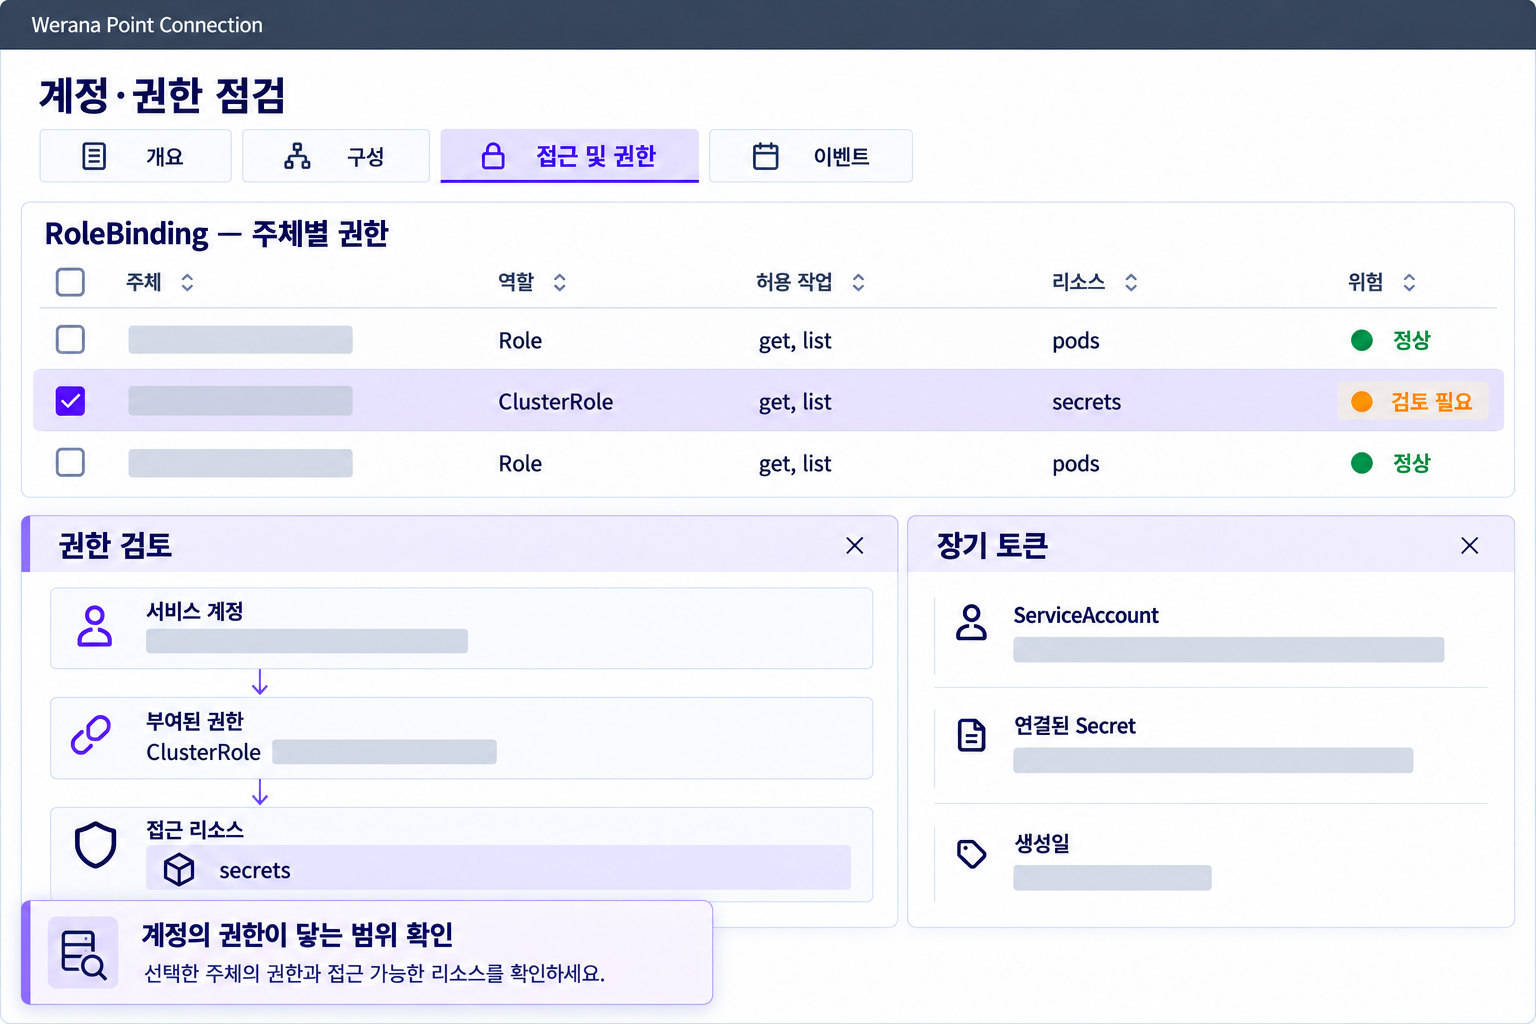
Trace service accounts to permissions and resources.

Follow RBAC relationships and authentication methods to review excessive permissions and credential-related risks.

Accounts & permissions — Trace service accounts to permissions and resources. (Korean UI mockup)
Werana Point Connection · Illustrative Korean interfaceView full-size image
  1. 01Service account
  2. 02Roles & permissions
  3. 03Accessible resources

01

Follow account access

Review Kubernetes ServiceAccount Non-Human Identity (NHI) through role-based access control (RBAC). Inspect resources and allowed actions in Role and ClusterRole permissions assigned through RoleBinding and ClusterRoleBinding using a least-privilege perspective.

02

Inspect long-lived tokens

Review long-lived tokens and related Secret metadata alongside their accounts and access targets. Identify credentials needing investigation without treating token age alone as proof of inactivity.

03

Review signals in observed traffic

Review credential-exposure signals in supported HTTP observation. Consider collected traffic, permissions and the observation period when selecting targets for further investigation.

Environment & coverage

What can you review in your environment?

Review the applicable scope based on your assets, collection permissions, and existing security operations.

Security categories to compareNHI · RBAC · IAM · CIEM

Accounts & permissions

Coverage focuses on Kubernetes service accounts, RBAC, and credentials visible within supported collection.

What to discuss

  • Kubernetes service-account and RBAC collection
  • Permissions to inspect tokens and credentials
  • Supported HTTP observation scope and period

FAQ

Frequently asked questions

Does no observed activity mean an account is unused?

Consider the observation period and collection coverage. Missing observations alone do not establish that an account is unused.

How do NHI, IAM and CIEM relate to RBAC checks?

NHI covers non-human identities such as services and workloads; IAM covers identity and access management; CIEM covers cloud infrastructure entitlements; and RBAC assigns access through roles. This service focuses on collected Kubernetes service accounts, bindings, roles and long-lived tokens. Confirm cloud-provider IAM coverage and integration status separately.

How do we assess excessive ServiceAccount permissions?

Inspect the Role or ClusterRole assigned through each RoleBinding or ClusterRoleBinding and the permitted actions and resources. Review cluster-admin relationships and long-lived-token evidence together. Missing activity alone does not establish that an account or permission is unnecessary.

Start with the scope that fits your environment.

Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.

Discuss identity review coverage