
01
Identify suspicious runtime activity
Runtime Security uses eBPF host observation to review execution, file and network activity in an intrusion detection (IDS) and host-based detection (HIDS) context.
WERANA / Services
Real-time threat detection
Review execution and network activity collected with eBPF, together with affected assets and the rules or indicators behind a detection.
Review workflow
Review execution, traffic, and privilege changes in context to identify signals worth investigating.
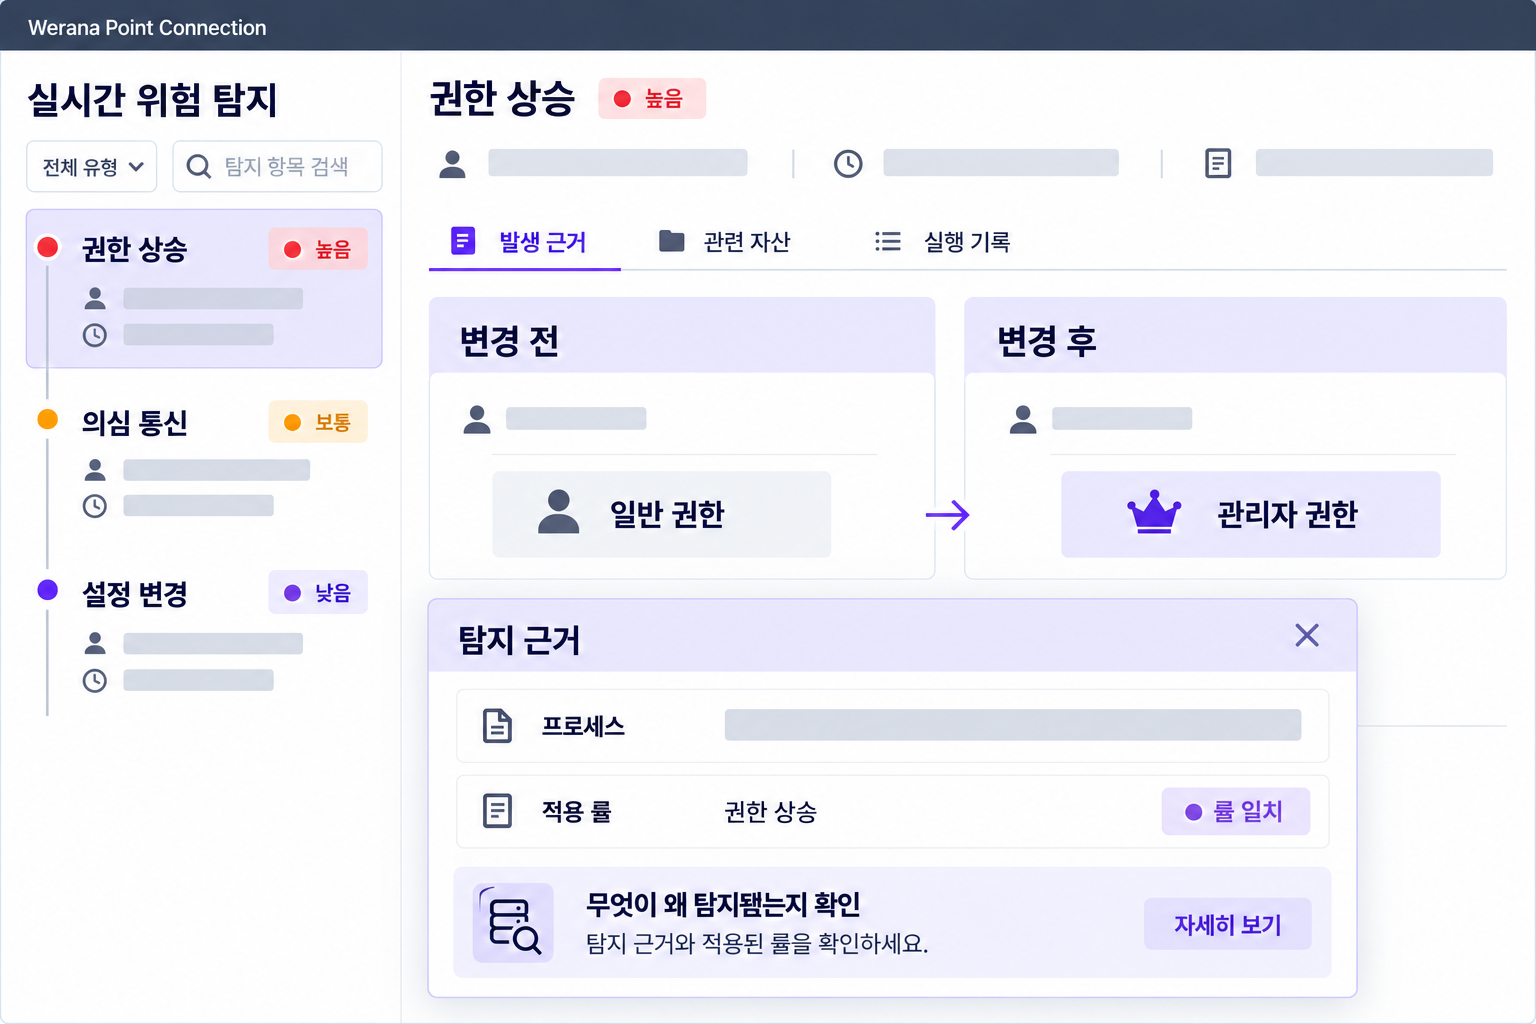
01
Runtime Security uses eBPF host observation to review execution, file and network activity in an intrusion detection (IDS) and host-based detection (HIDS) context.
02
Review the occurrence time and affected assets alongside MITRE ATT&CK tactics, techniques, indicators (IOC) and detection evidence.
03
Review event Correlation, File Integrity Monitoring (FIM) and configuration-change detection against enabled rules and their required collection sources.
Environment & coverage
Review the applicable scope based on your assets, collection permissions, and existing security operations.
Security categories to compareIDS · HIDS · NIDS · IPS · HIPS · EDR · NDR · CWPP
Coverage depends on supported operating systems, kernels, collection capabilities, and enabled rules.
FAQ
Detection results identify collected activity matching enabled rules or indicators.
IDS detects signs of intrusion; HIDS focuses on host activity, while NIDS focuses on network traffic. IPS and HIPS also concern how attacks are prevented or blocked. This service describes eBPF host observation and detection using enabled rules and indicators. Executing a response command must be assessed separately from a network IPS blocking attacks in the traffic path.
EDR concerns endpoint detection and response; NDR concerns network detection and response; and CWPP concerns cloud workload protection. Compare supported operating systems and kernels, process, file and traffic collection, rules and response actions. A detection capability in one area does not establish the complete scope of each product category.
Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.