
01
Compare settings with the baseline
Compare baseline and observed settings through Kubernetes Security Posture Management (KSPM) and supported server CIS Benchmark checks.
WERANA / Services
Security configuration
Review Kubernetes security settings and supported server checks alongside configuration evidence and policy coverage.
Review workflow
Inspect server and Kubernetes baselines and identify targets outside the collected policy scope.
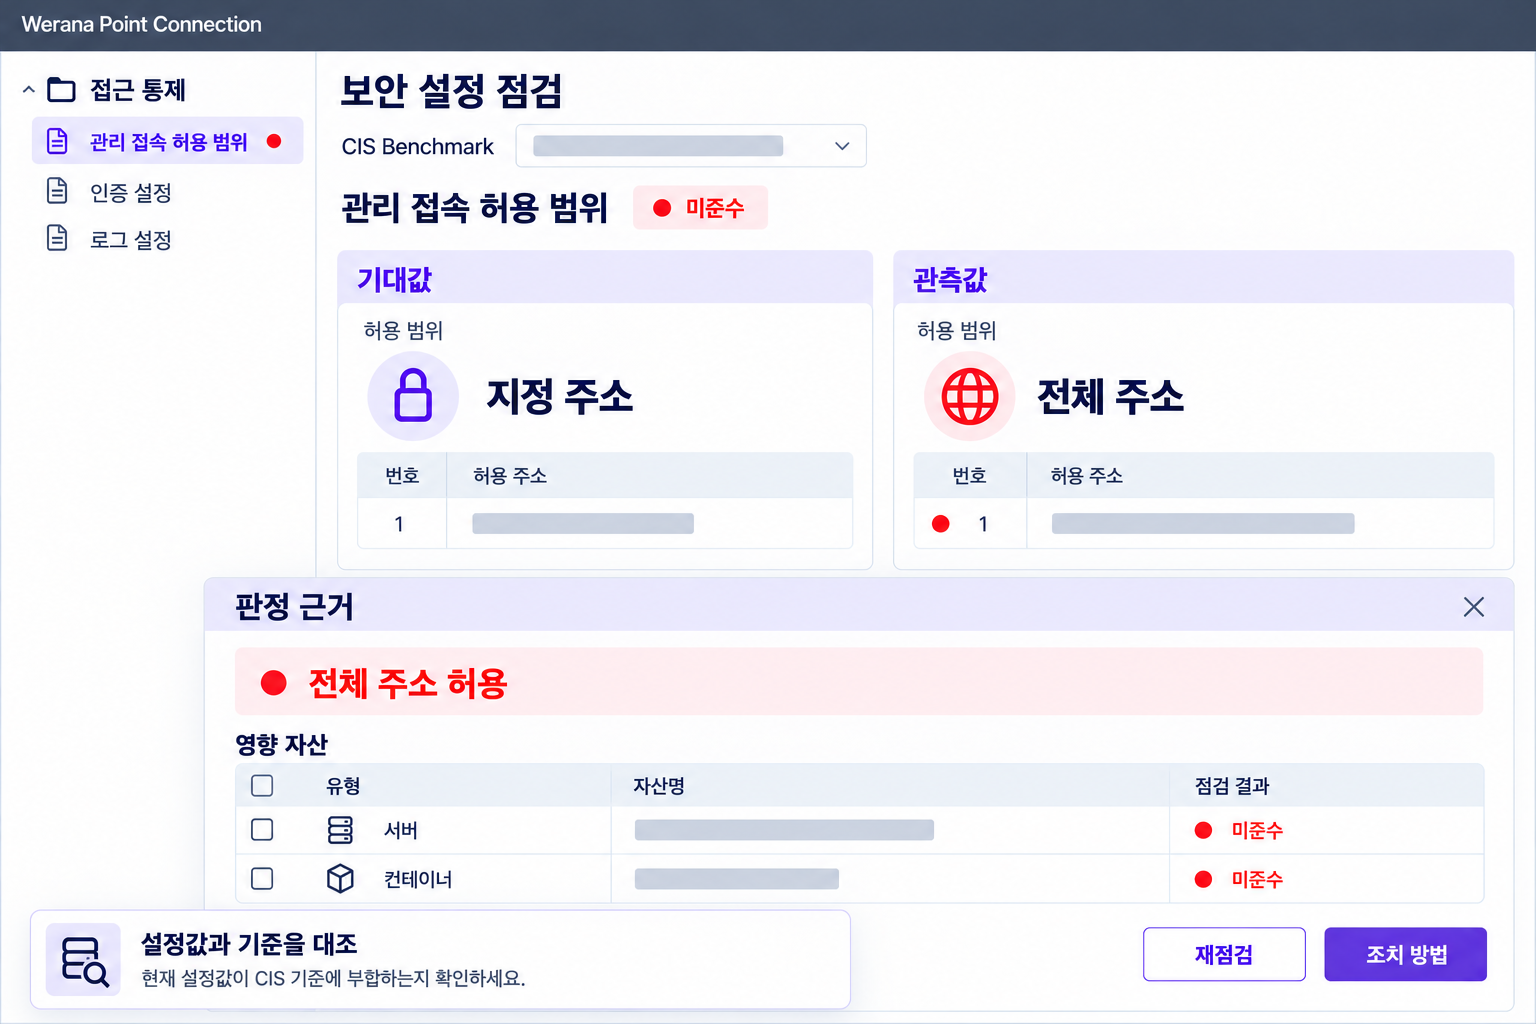
01
Compare baseline and observed settings through Kubernetes Security Posture Management (KSPM) and supported server CIS Benchmark checks.
02
Review NetworkPolicy target coverage separately from Ingress TLS settings to understand network policy and transport-protection scope.
03
Inspect Security Context evidence, including Privileged Container settings, root-execution conditions and Linux Capabilities. Review remediation guidance for failed checks and re-evaluate after changes.
Environment & coverage
Review the applicable scope based on your assets, collection permissions, and existing security operations.
Security categories to compareCSPM · KSPM · CWPP · CNAPP
Supported checks and collection permissions differ between servers and Kubernetes environments.
FAQ
The presence and scope of a setting differ from its actual effect. Review observations alongside configuration.
CSPM concerns cloud-resource security configuration; KSPM concerns Kubernetes configuration and compliance; CWPP concerns workload protection; and CNAPP integrates these areas. This page describes supported server and Kubernetes checks. Confirm provider-specific resource checks and integrations for AWS, Azure, GCP and other environments separately.
A setting's presence, its selected targets and its observed effect are different questions. Inspect NetworkPolicy selectors and ingress and egress conditions separately from Ingress TLS. Privileged and root-execution Security Context checks address a separate part of the security configuration.
Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.