
01
Identify checks needing attention
Use Control Mapping to connect supported ISMS-P and CIS criteria with technical evaluation evidence.
WERANA / Services
Compliance & audit
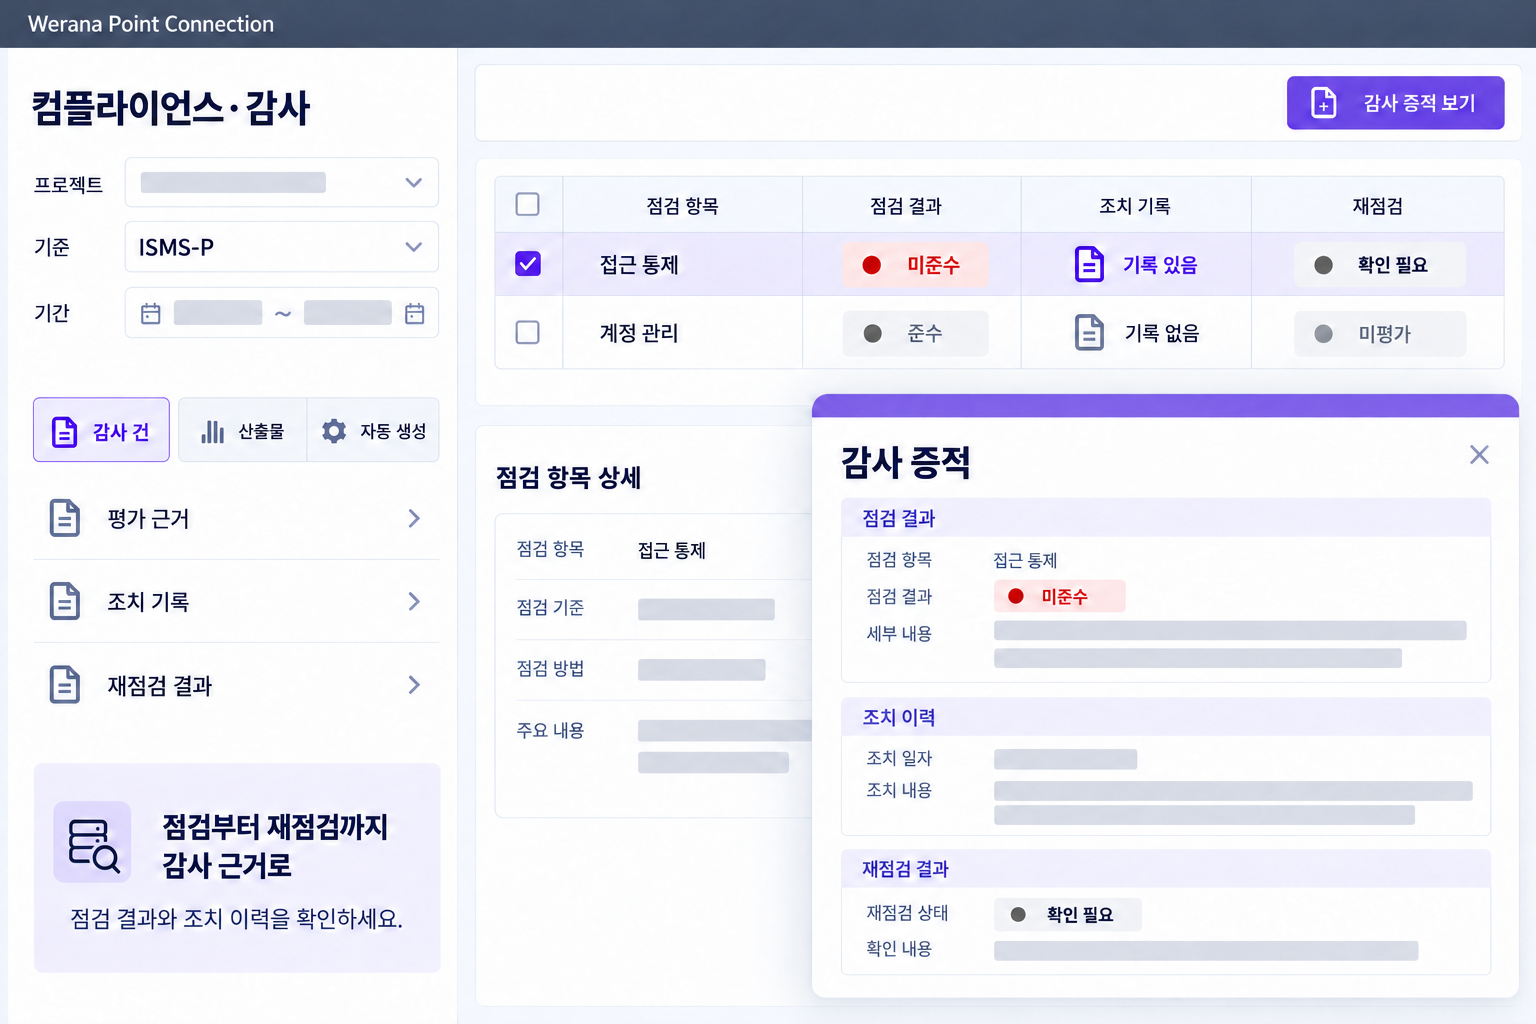
Connect failed checks with remediation, exceptions, and rechecks. Organize evidence by project, standard, and period.
Review workflow
Connect failed checks, remediation, exceptions, and rechecks, then organize evidence for the scope you need.
01
Use Control Mapping to connect supported ISMS-P and CIS criteria with technical evaluation evidence.
02
Connect Remediation, approved Exceptions and rechecks through an Audit Trail, keeping work records separate from evaluation results.
03
Review Evidence Package generation and verification history and SHA-256 comparisons to assess submission-file integrity alongside package and ledger status.
Environment & coverage
Review the applicable scope based on your assets, collection permissions, and existing security operations.
Security categories to compareGRC · ISMS-P · N2SF · STIG · NIST · ISO 27001 · PCI DSS
Technical checks, control mappings, and evidence-generation conditions depend on the supported standard and configuration.
FAQ
A work record documents the action taken. A recheck provides a new evaluation result that can be linked to audit evidence.
GRC is a broad governance, risk and compliance discipline. ISMS-P, N2SF, STIG, NIST, ISO 27001 and PCI DSS have different purposes and scopes. Apply this service based on the standards, control mappings, technical checks and evidence actually supported. An N2SF asset grade or a standard reference on a rule does not establish complete framework coverage, compliance or certification.
It compares the expected SHA-256 with the actual stored-file hash and checks related ledger consistency. File integrity and security-control compliance are separate assessments. Remediation records still need recheck results, and an evidence package does not guarantee certification or an audit outcome.
Tell us about your environment and security priorities. We will help review supported capabilities and collection requirements.